Enterprise SSO / OIDC / SAML identity and access management
Tech Specifications
Trust & License
Keycloak is an open-source identity and access management (IAM) server that centralizes authentication and authorization for web apps, mobile apps, and APIs. Built on Quarkus, it lets you add single sign-on (SSO) to applications with little to no code, so users authenticate against Keycloak rather than against each individual app.
It implements the standard protocols OpenID Connect, OAuth 2.0, and SAML 2.0, and offers user federation against LDAP and Active Directory, identity brokering with external providers (Google, GitHub, social logins), fine-grained authorization, multi-factor authentication, and self-service account management. Realms provide multi-tenant isolation, and an admin console plus REST API handle configuration of clients, roles, groups, and users.
Typical use is as a shared authentication backend for an organization's internal and customer-facing applications: deploy Keycloak once, register each application as a client, and delegate login, token issuance, and session management to it. It is commonly backed by a PostgreSQL or MySQL database in production and sits behind a reverse proxy with TLS.
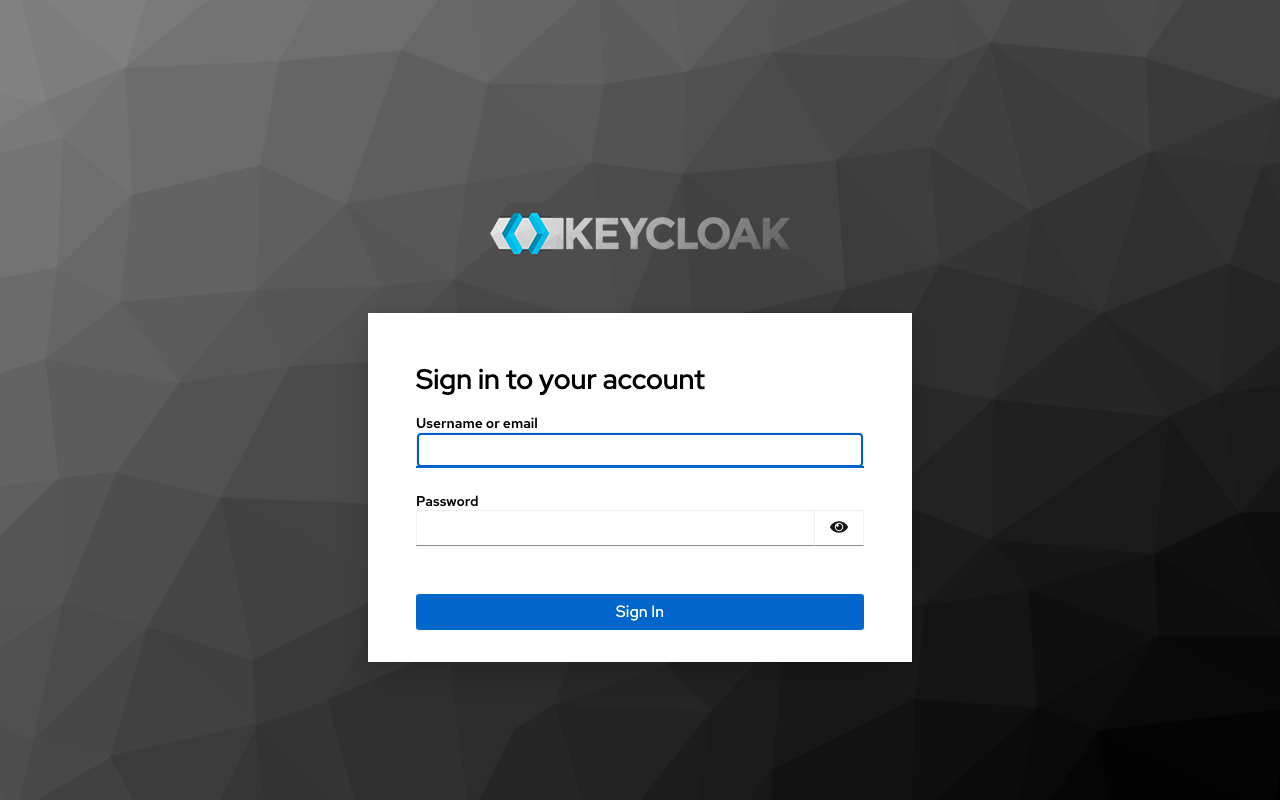
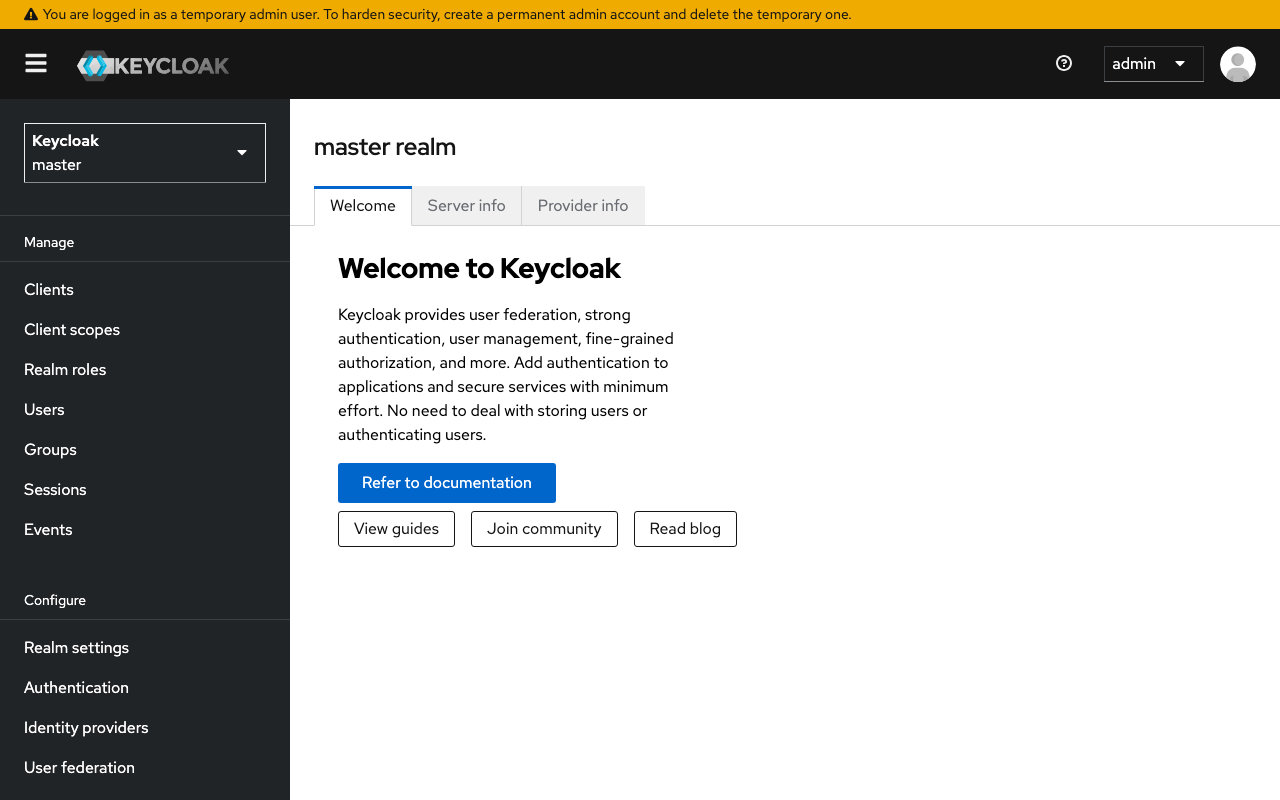
Screenshots
Install on Hop3
hop3 catalog install keycloak-nixgen
Build paths
The same application, packaged different ways. The default is the one tested most; pick another if you have a reason to.